What HTTPS did for the Internet, Zama is doing for Onchain Finance
Following our report on Zama, “A Look Into Confidential DeFi,” Ryan Celaj, our head of research, and Kyle Cai, our former senior research analyst, sat down with the company’s CEO and co-founder, Rand Hindi.
Zama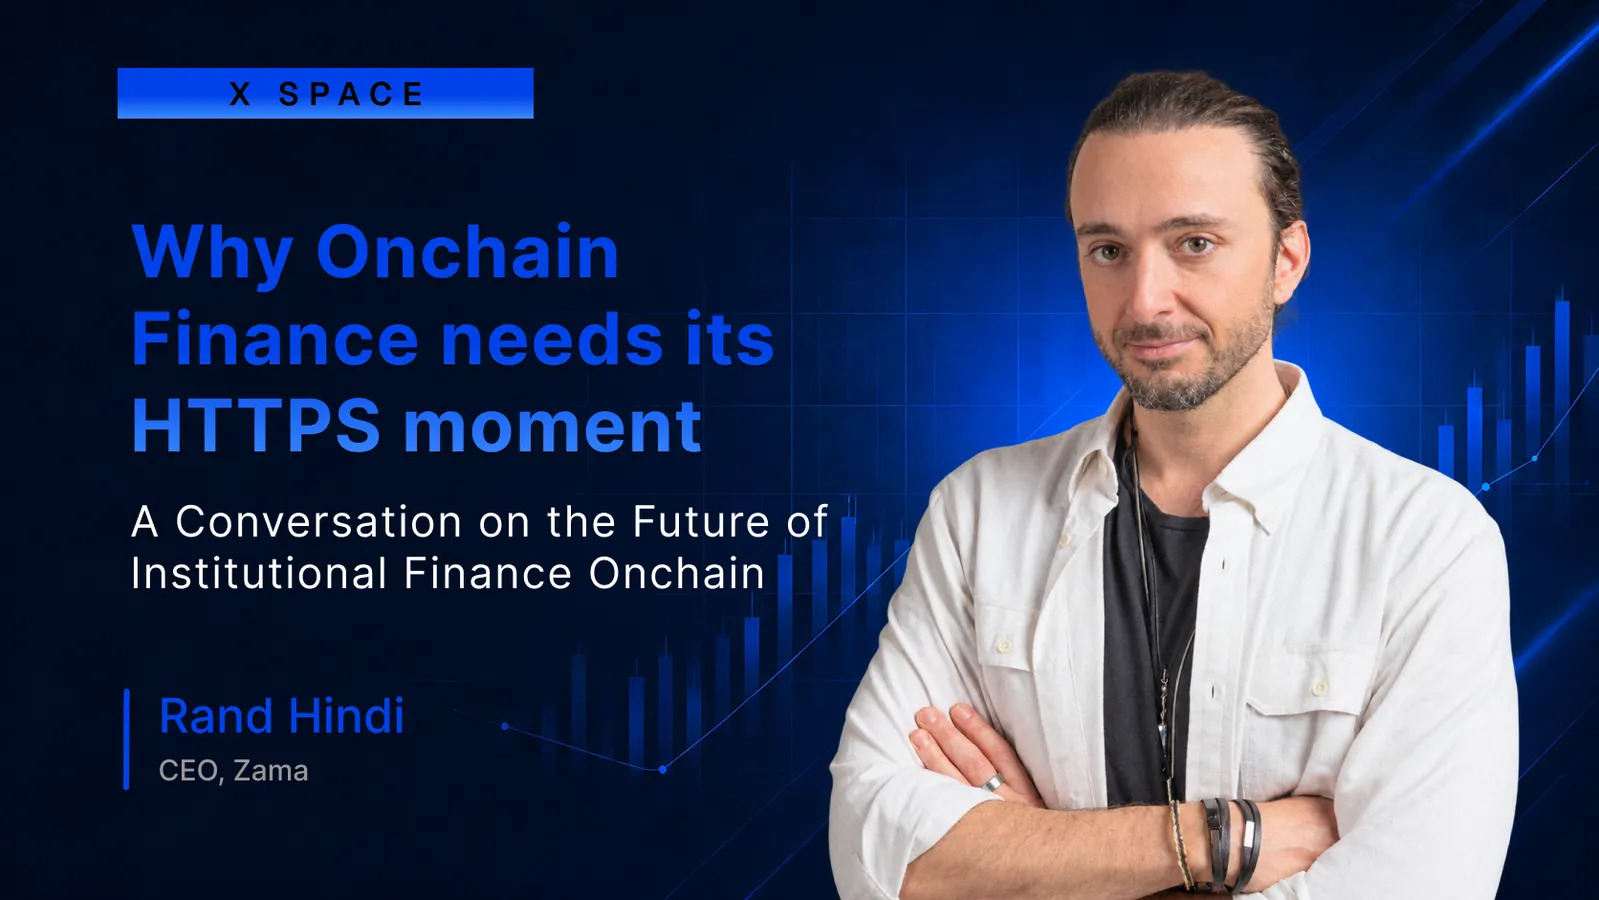
Following our report on Zama, “A Look Into Confidential DeFi,” Ryan Celaj, our head of research, and Kyle Cai, our former senior research analyst, sat down with the company’s CEO and co-founder, Rand Hindi. They discussed Zama’s unexpected foray into crypto, its competitors’ approach to encrypting blockchain data, the “AI apocalypse,” and much more. This conversation has been edited for length and clarity. You can find the full interview here.
1. A confidentiality layer for onchain finance
Ryan Celaj: For anyone new to Zama, what are you building and why does it matter?
Rand Hindi: My background is in AI. I did a PhD at 21, built one of the first AI companies, and sold it in 2019. Since 2020, I've been building Zama with my co-founder Pascal Paillier, a pioneer of Homomorphic Encryption. I've also been in crypto for over a decade.
Zama is a confidentiality layer for onchain finance. It lets you pay, trade, invest, and put money in vaults on public blockchains like Ethereum and Solana without everyone seeing what you're doing.
A good analogy is, what HTTPS did for the internet, we're doing for onchain finance.
2. Who confidential vaults are for
Kyle Cai: You started with a Steakhouse Financial confidential USDC vault and have since expanded to 16 vaults across five curators: Steakhouse Financial, Armitage by Wintermute, Flowdesk, Rockaway, and Bitwise.
Ryan Celaj: Who are those vaults built for? Retail or institutions?
Rand Hindi: The people who need privacy most onchain are those with large positions. This isn't about hiding what you buy with your credit card. It's about making sure competitors and other funds can't see how you trade or allocate your portfolio.
Vaults are one piece of the puzzle. People put money in vaults, but they also want to trade and build strategies, and they need confidentiality for all of it. That's what we're building out now.
3. Why finance needs its HTTPS moment
Ryan Celaj: Interest in privacy has grown a lot over the last two years. Is that because institutions are coming onchain?
Rand Hindi: Pretty much. We didn't start as a blockchain company. We started as a cryptography company working on Fully Homomorphic Encryption. Exploring use cases, we concluded that if finance moves onchain, confidentiality becomes necessary. Today, only people who have no choice or don't care about exposure use public blockchains. Most of finance never will without confidentiality.
We've seen this before. In the early internet, every message, website visit, and credit card number was visible to anyone watching the network. That's where public blockchains are today. HTTPS was created largely so people could pay online safely, and it ended up enabling far more than payments.
We're starting by making financial transactions confidential. Eventually, that opens a design space for applications that couldn't exist otherwise.
4. FHE vs. ZK
Ryan Celaj: What is FHE, and how is it different from ZK? You've called Zcash "encrypted gold" and Zama "encrypted Ethereum."
Rand Hindi: FHE lets you compute on encrypted data. If you add two encrypted numbers A and B, decrypting the result gives you A plus B. You never see the data you're computing on.
For smart contracts, that means both onchain state and transaction data can stay encrypted while the code still runs and remains publicly verifiable. That's why it fits blockchains so well.
FHE also gives you auditability. With some shielded-pool designs, it's hard to verify in real time that a bug wasn't used to create funds. With FHE, we can verify the encrypted supply. And if FHE were ever broken, the main impact would be on privacy rather than on the integrity of the supply.
We launched confidential vaults at the end of June. Within about three months, shielded TVL passed 130 million. For onchain finance, FHE is the right tool.
5. RWAs and the scale of TradFi
Kyle Cai: What surprised me most was Apex Group targeting $100 billion of tokenized assets on T-REX by 2027, with Zama for confidentiality. [Ed. note: In March 2026, Zama became the native confidentiality layer for T-REX Ledger, the RWA infrastructure backed by Apex Group.] What does that partnership mean?
Rand Hindi: It shows how different the scale is. Across all privacy protocols today, shielded value is measured in hundreds of millions to a few billion dollars. Even a single-digit percentage of what T-REX aims to tokenize would be larger than that.
You can read that as "that's amazing," or as "we're very early." DeFi has been talking in billions for five or six years. TradFi thinks in trillions. As those assets move onchain, I believe most of them will eventually be confidential, just as most internet traffic is encrypted today. That's a multi-year journey.
6. From one vault to millions
Kyle Cai: Beyond TVL, what drives Zama's next stage of growth?
Rand Hindi: Vaults. Take a private bank. You ask your banker for something better than T-bill yields. They come back with a strategy, say market-neutral, with your money locked for three months. But you can't use that position as collateral elsewhere, or combine strategies from different banks into one portfolio.
Now imagine each strategy is a vault onchain. You can compose vaults into a meta-strategy no single bank could offer. That's a new paradigm of composable investment products. I expect many more vaults over the next few years: tokenized stock strategies, tokenized funds, permissioned and permissionless. Confidentiality is essential for that to happen.
7. Compliance by design
Ryan Celaj: How do you think about compliance as privacy comes onchain?
Rand Hindi: There are two sides. First, whether a product should be regulated is the issuer's decision, not Zama's. Whoever launches a vault or an RWA decides whether it needs to be permissioned or KYC'd.
Second is privacy itself. We settled on a middle ground: nobody onchain sees your amounts or balances, but the service provider can. A confidential stablecoin issuer, for example, can see transactions using its stablecoin so it can meet AML and counter-terrorism obligations.
We're not protecting you from issuers. We're protecting you from competitors and front-runners. We deliberately don't hide sender and recipient, only amounts and balances, which keeps traceability possible if there's an issue.
Zama is built for compliant financial infrastructure, and institutions want tools designed to support compliance. The only way to make most onchain transactions confidential is to do it legally.
8. What's next
Ryan Celaj: Anything you can tease for the DefiLlama audience?
Rand Hindi: Two things matter right now. The first is security. With AI and, eventually, quantum, cybersecurity has never mattered more, and I think it's the biggest risk for all of crypto in the coming months. We invest heavily in audits and AI-assisted security research. The second is utility. Beyond growing TVL, we want shielded assets to be used: confidential swaps, more vaults, more integrations. Anything you can do financially onchain, you should be able to do confidentially, with the same or better execution.
Get started
Read DefiLlama's report: A Look Into Confidential DeFi
Explore Zama's confidential vaults: https://app.zama.org/earn
Follow Zama on X for updates
Confidential onchain finance is just getting started.